Introduction to web pentesting: where to start
Originally published on Bemorex Learn, our learning platform. · Leer en español
What is pentesting?
Pentesting (penetration testing) is the process of evaluating the security of a computer system by simulating a real attack. The goal is to find vulnerabilities before a malicious attacker does.
Prerequisites
Before getting into pentesting, you need a solid foundation in networking, HTTP/HTTPS protocols, Linux operating systems, and basic programming (Python or Bash).
OWASP Top 10
The OWASP Top 10 is a list of the most critical web vulnerabilities. It includes SQL injection, cross-site scripting (XSS), broken authentication, and more. It is the starting point for every web pentester.
SQL Injection
SQL injection allows an attacker to execute malicious queries against the database. It is one of the oldest vulnerabilities but remains extremely common.
Cross-Site Scripting (XSS)
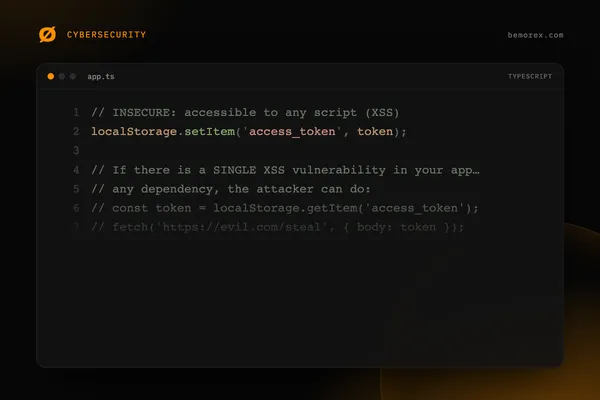
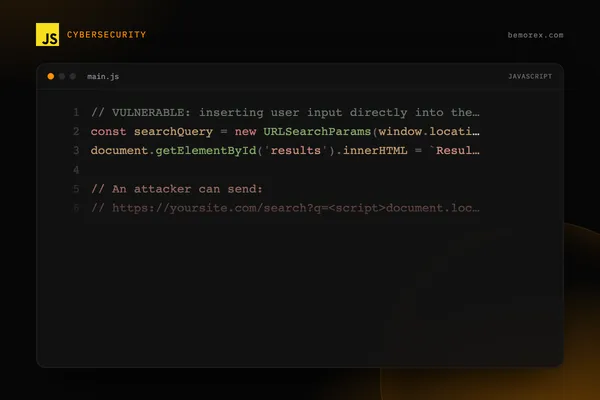
XSS allows injecting malicious scripts into web pages that other users visit. It can be reflected, stored, or DOM-based.
Essential tools
The basic tools of every web pentester include Burp Suite, Nmap, Nikto, SQLMap, and Gobuster. Kali Linux comes with most of them pre-installed.
Where to practice legally
Platforms like HackTheBox, TryHackMe, PortSwigger Web Security Academy, and DVWA offer safe environments to practice pentesting legally and ethically.
Code examples
Bash
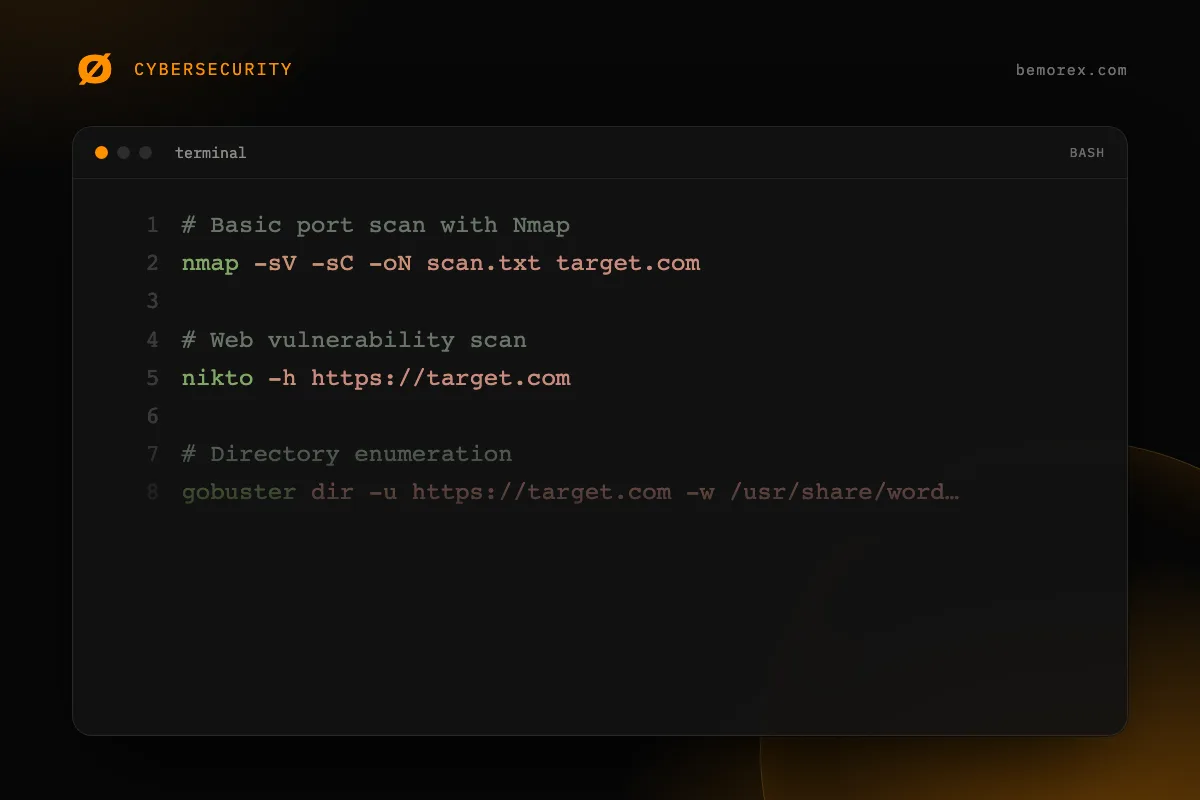
# Basic port scan with Nmap
nmap -sV -sC -oN scan.txt target.com

# Web vulnerability scan
nikto -h https://target.com

# Directory enumeration
gobuster dir -u https://target.com -w /usr/share/wordlists/common.txt